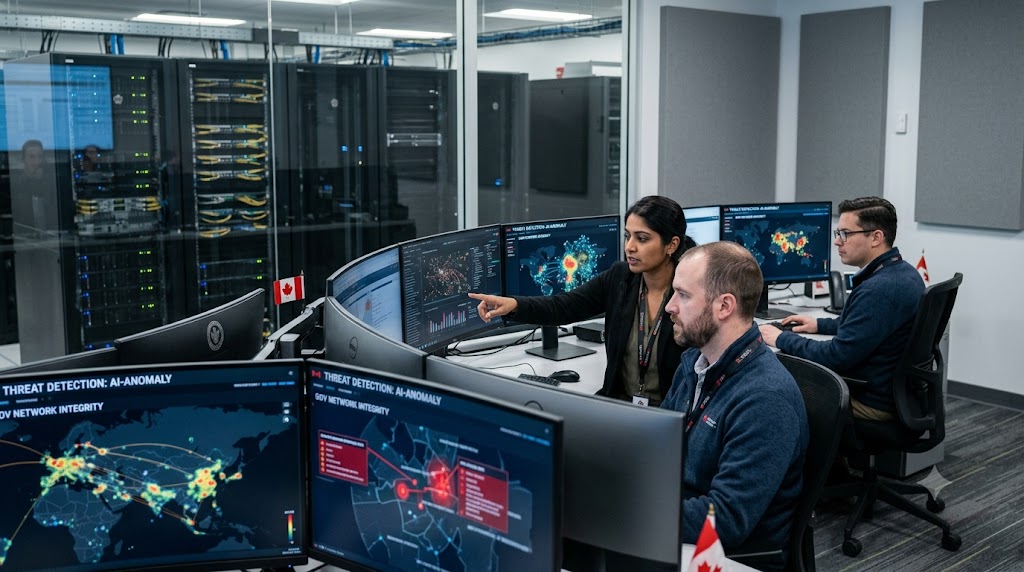
OTTAWA — October 10, 2026 The Canadian government has introduced updated cybersecurity requirements for federal departments and agencies as advanced artificial intelligence creates new challenges for protecting digital infrastructure.
The directive, effective October 1, 2026, instructs federal organizations to apply baseline cybersecurity controls consistently and identify weaknesses that could be exploited by AI-enabled threat actors. It also calls for an “assume breach” approach, emphasising rapid containment, damage limitation and recovery when security incidents occur.
The requirements cover a broad range of government technology, including servers, workstations, mobile devices, cloud environments, network equipment and connected laboratory systems.
The policy reflects growing concern that AI could help attackers identify vulnerabilities and conduct cyber operations at greater speed. Federal organizations are expected to strengthen their defences and address significant gaps rather than relying solely on traditional security measures.
The directive marks a significant step in Canada’s approach to AI-era cybersecurity, with implications for public-sector IT teams, government technology suppliers and cybersecurity service providers.
The policy applies to federal government systems; it is not a blanket new cybersecurity law for every Canadian business.
Comments (0)
Sign in to join the conversation.